Greece will ban children under the age 15 from using social media starting next year. Prime Minister Kyriakos Mitsotakis made the announcement in a video posted to TikTok, in which he referenced anxiety, sleep problems and addictive design features as reasons for the ban.
Greece has been proactive in its approach to tackling excessive screen time for children, having already banned mobile phones in schools in 2024. While the PM chose not to name any platforms, he said he was concerned about children comparing themselves to others on social media and taking online comments to heart.
"Greece will be among the first countries to take such an initiative," Mitsotakis said. "I am certain, however, that it will not be the last. Our goal is to push the European Union in this direction as well."
As reported by The New York Times, Greece’s digital governance minister, Dimitris Papastergiou, said that social media companies would be legally required to uphold the new restrictions by verifying the ages of their users. Failure to comply would lead to fines under the EU’s Digital Services Act. Parents would also need to download an app called Kids Wallet, backed by the state, that could be paired to their child’s device and block access. The finer details of how the ban would be enforced are still being worked out by decision-makers.
The PM conceded that he would likely incur the wrath of his country’s young children, but there’s widespread support for the plans from Greece’s adult population, according to an opinion poll published by ALCO in February. Greece follows in the footsteps of Indonesia, Austria and Australia, all of which have introduced similar bans of their own in the last year. The UK is also considering bringing in tighter restrictions on children under the age of 16 using social media.
This article originally appeared on Engadget at https://www.engadget.com/social-media/greece-will-ban-all-kids-under-15-from-using-social-media-154850415.html?src=rss
A smartphone displays a folder of social media applications, including TikTok, Instagram, Facebook, X, Snapchat, and YouTube, with a blurred ''no under-16'' sign in the background, in Creteil, France, on March 31, 2026. Australia's eSafety Commission warns social media platforms about their failure to enforce the country's ban on under-16 users. (Photo by Samuel Boivin/NurPhoto via Getty Images)
The Islamic Revolutionary Guard Corps (IRGC), a branch of Iran's armed forces, has threatened to target US tech companies' operations in the Middle East. It told employees of 18 companies — including Apple, Google, Meta and NVIDIA — “to leave their workplaces immediately to save their lives,” as CBS Newsreported. Those living close to the companies' facilities in the region were instructed to evacuate immediately as well. Microsoft, Oracle, Tesla, HP, Intel, Palantir, Boeing, Dell, Cisco and IBM are also among the companies that the IRGC named.
"Since the main element in designing and tracking terror targets are American [information and communications technology] and AI companies, in response to this terrorist operation, from now on the main institutions effective in terrorist operations will be our legitimate targets," the IRGC said in a statement. The military force warned it will start targeting the companies on Wednesday evening if more Iranian leaders are killed.
Iran previously pledged to attack companies and banks tied to the US and Israel, though the warning it issued on Tuesday had a specific deadline. Earlier this month, Iranian drones struck Amazon data centers in Bahrain and the United Arab Emirates, disrupting Amazon Web Services operations in the region.
The US reportedly used Anthropic's AI in its initial airstrikes against Iran at the onset of the war in late February. Israel has been using a new AI platform of its own to help it track the movements of Iranian officials.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/iran-threatens-imminent-attacks-on-us-tech-companies-in-the-middle-east-184841155.html?src=rss
The White House has announced a new AI policy framework that calls for Congress to craft federal regulation that overrules state AI laws. The Trump administration has made multiple attempts to overrule more restrictive state-level AI regulation, but has failed so far, most notably in the passing of the “One Big Beautiful Bill.”
The framework focuses on a variety of topics, covering everything from child privacy to the use of AI in the workforce. “Importantly, this framework can succeed only if it is applied uniformly across the United States,” The White House writes. “A patchwork of conflicting state laws would undermine American innovation and our ability to lead in the global AI race.”
In terms of child privacy protections, the framework ask for Congress to require companies to provide tools like “screen time, content exposure and account controls” while also affirming that “existing child privacy protections apply to AI systems,” including limits on how data is collected and used for AI training. The framework also says carveout states should be allowed to enforce “their own generally applicable laws protecting children, such as prohibitions on child sexual abuse material, even where such material is generated by AI.”
The energy-use and environmental impact of AI infrastructure is a going concern, but the White House’s policy proposals are primarily worried about the cost of data centers. The framework suggests federal AI regulation should make sure that higher electricity costs aren’t passed on to people living near data centers, while streamlining the process for permitting AI infrastructure construction, so companies can pursue “on-site and behind-the-meter power generation.” The framework also calls for fewer restrictions on the software-side of AI development, proposing “regulatory sandboxes for AI applications” and asking Congress to “provide resources to make federal datasets accessible to industry and academia in AI-ready formats.”
While a recently AI bill from Senator Marsha Blackburn (R-Ten.) attempts to eliminate Section 230, a piece of a larger law that says platforms can’t be held responsible for the speech they host, the framework appears to propose the opposite. “Congress should prevent the United States government from coercing technology providers, including AI providers, to ban, compel or alter content based on partisan or ideological agendas,” the White House writes. The framework is similarly hands-off when it comes to copyright and the use of intellectual property to train AI. “Although the Administration believes that training of AI models on copyrighted material does not violate copyright laws,” the White House writes, it supports the issue being settled in court rather than by legislation. Though, the White House does think Congress should “consider enabling licensing frameworks” so IP holders can bargain for compensations from AI providers.
The clincher in the White House’s proposal is the idea that federal regulation should preempt state law, specifically so that states don’t “regulate AI development,” don’t “unduly burden American’s use of AI for activity that would be lawful if performed without AI” and don’t punish AI companies “for a third party’s unlawful conduct involving their models.” The idea that AI companies aren’t liable for the illegal or harmful uses of their products is particularly problematic because it lies at the heart of multiple intersecting issues with AI right now, including it being used to generate sexually explicit images of children and allegedly playing a role in the suicide of users.
Ultimately, though, the framework might be too contradictory to be useful, Samir Jain, the Vice President of Policy for the Center for Democracy and Technology, writes in a statement to Engadget:
The White House’s high-level AI framework contains some sound statements of principles, but its usefulness to lawmakers is limited by its internal contradictions and failure to grapple with key tensions between various approaches to important topics like kids’ online safety. It rightly says that the government should not coerce AI companies to ban or alter content based on ‘partisan or ideological agendas,’ yet the Administration’s ‘woke AI’ Executive Order this summer does exactly that. On preemption, the framework asserts that states should not be permitted to regulate AI development, but at the same time rightly notes that federal law should not undermine states’ traditional powers to enforce their own laws against AI developers. States are currently leading the fight to protect Americans from harms that AI systems can create, and Congress has twice correctly decided not to pursue broad preemption.
President Donald Trump has attempted to have an active role in how AI is developed and regulated in the US with mixed results, primarily because, as Jain notes, Congress has been unwilling to give up states’ right to regulate the technology on their own terms. Without that, its hard to say how much of the framework will actually make it into federal law.
This article originally appeared on Engadget at https://www.engadget.com/ai/the-white-house-proposes-new-ai-policy-framework-that-supersedes-state-laws-192251995.html?src=rss
California, Massachusetts, Connecticut and New York are leading a group of 20 other states in suing the US Environmental Protection Agency for renouncing its ability to regulate greenhouse gas emissions, The New York Times reports. The lawsuit specifically argues that the EPA's decision to rescind a 2009 study that determined greenhouse gases are dangerous to public health was illegal. The study, which is the source of what's called the "Endangerment Finding," was one of several justifications — along with things like the Clean Air Act — for the agency's ability to regulate emissions.
Rescinding the finding nullified the EPA's evidence for things like emissions standards and a variety of other regulations that attempted to reduce the amount of greenhouse gases produced by the automotive, coal and oil industries. The Trump administration framed the rollback as a cost-saving measure, but it was also a major blow to the government's ability to fight climate change. Greenhouse gases, which include things like carbon dioxide, methane and nitrous oxide, collect in the atmosphere and warm the planet, upsetting weather patterns and negatively impacting the environment. Determining the changes caused by greenhouse gases posed a risk to public health gave the EPA the authority to regulate them under its existing mandate to address air pollution. An authority it could have again, depending on the result of this litigation.
Of course, winning a lawsuit isn't necessary to restore the EPA's role in fighting climate change. Congress could do that now by passing a new law. The legal route is just faster, and potentially riskier. The New York Times writes that this new lawsuit was filed in the US Court of Appeals for the District of Columbia, and could ultimately be combined with an existing lawsuit from environmental groups. Depending on how the case fairs in the lower court, it may eventually be appealed to the US Supreme Court, who could decide on an even more restrictive interpretation of the EPA's role.
This article originally appeared on Engadget at https://www.engadget.com/science/states-are-suing-the-epa-for-relinquishing-its-role-as-a-greenhouse-gas-emissions-regulator-221425064.html?src=rss
The Pentagon is making plans to have AI companies train versions of their models specifically for military use on classified information, according to the MIT Technology Review. If true, it wouldn’t come as a surprise, seeing as the US is aiming to become an “AI-first" warfighting force, based on the statement [PDF] released by Secretary of Defense Pete Hegseth earlier this year.
The department is already using AI models in the military: For instance, the US reportedly used Anthropic’s Claude to help with the capture of Venezuelan President Nicolás Maduro and with its attack on Iran, even after President Trump ordered federal agencies to ban its technology. But models trained on actual classified data could give more accurate and detailed responses, say, for situations similar to what happened in the past that aren’t public information.
MIT Tech Review says the department is looking to conduct the training in a secure data center that’s allowed to host classified government projects. The Pentagon would train copies of AI models, but it would remain the only owner of any data used for training. In rare cases, someone from the AI company could be granted the appropriate security clearance to see classified information.
Aalok Mehta, who previously led AI policy efforts at Google and OpenAI, told the publication that training models on classified data carries certain risks. It’s not that the information could go public, since the the models trained would be versions made specifically for military purposes. However, if the same model is used across the whole Defense Department, for instance, personnel without the correct clearance level could end up getting information that they weren’t supposed to have access to.
If the initiative pushes through, the department would likely be training models from OpenAI and xAI, which recently signed agreements with the agency. Anthropic, which has long worked with the government, might not be part of this project. The company refused to allow its technology to be used for mass surveillance and the development of autonomous weapons, and Trump ordered all federal offices to ban it as a result.
This article originally appeared on Engadget at https://www.engadget.com/ai/the-defense-department-reportedly-plans-to-train-ai-models-on-classified-military-data-120332113.html?src=rss
The Department of Defense said giving Anthropic continued access to its warfighting infrastructure would “introduce unacceptable risk” to its supply chains in a court filing submitted in response to the AI company’s lawsuit. If you’ll recall, Anthropic sued the government to challenge the supply chain risk designation it received for refusing to allow its model to be used for mass surveillance and the development of autonomous weapons.
In its filing, the department explained that its secretary, Pete Hegseth, had a provision incorporated into AI service contracts, allowing the agency to use their technologies for any lawful purpose. Anthropic refused its terms and apparently, the company’s behavior caused the Pentagon to question whether it truly was a “trusted partner” that it could work with when it comes to “highly sensitive” initiatives. “After all, AI systems are acutely vulnerable to manipulation, and Anthropic could attempt to disable its technology or preemptively alter the behavior of its model either before or during ongoing warfighting operations, if Anthropic — in its discretion — feels that its corporate “red lines” are being crossed,” the Pentagon wrote in its filing. “DoW deemed that an unacceptable risk to national security,” it added, referring to the agency as the Department of War, which is the Trump administration’s preferred name for it.
It was due to those concerns that President Trump ordered federal agencies to stop using its technology, the filing reads. The company is asking the court to issue a preliminary injunction and put a pause on a ban while it’s challenging its supply chain risk designation in court. While Anthropic’s clients could continue working with the company on non-defense-related projects, it says the label could cause it to lose billions of dollars in revenue. It’s not quite clear if Anthropic is still trying to reach a new deal with the government, as was reported before it filed its lawsuit. As The New York Timesnotes, Microsoft, Google and OpenAI had filed friend-of-the-court briefs in support of Anthropic since then.
This article originally appeared on Engadget at https://www.engadget.com/ai/defense-department-says-anthropic-poses-unacceptable-risk-to-national-security-094328717.html?src=rss
There may have been some extra incentive for the Trump administration to get the TikTok US deal done. According to a report from The Wall Street Journal, the Trump administration is set to receive a total of $10 billion in the deal that allowed TikTok to remain in the US. The new investors who acquired stakes in the US entity of TikTok already paid a $2.5 billion fee to the administration when the deal closed in January, but WSJ's latest report noted that the group of investors would continue to make payments until the total hits $10 billion.
After a group of investors, which includes Oracle along with the Silver Lake and MGX investment firms, acquired stakes in the US-based TikTok entity called TikTok USDS Joint Venture, the WSJ previously reported that the administration would receive a "multibillion-dollar fee" for its work on the deal. To better contextualize the recently-revealed $10 billion fee the Trump administration is receiving, the US entity of TikTok was valued at $14 billion by Vice President JD Vance.
The Trump administration has previously involved itself in major deals with other US corporations. Last year, the administration invested $8.9 billion into Intel and received a nearly 9 percent equity stake. In terms of unprecedented windfalls, the Trump administration also received a Boeing 747-8 as a gift from the Qatari government in May.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/trump-administration-will-reportedly-get-10-billion-for-brokering-the-tiktok-deal-180954979.html?src=rss
Google is rolling out Gemini AI agents to the Department of Defense's more than 3 million civilian and military employees, according to Bloomberg. The agents will initially operate on unclassified networks, with talks underway to expand them to classified and top-secret systems, according to Emil Michael, the Under Secretary of Defense for Research and Engineering.
Eight pre-built agents will automate tasks like summarizing meeting notes, building budgets and checking proposed actions against the national defense strategy. Google Vice President Jim Kelly said in a blog post on Tuesday that Defense Department personnel can also create custom agents using natural language.
Google's AI chatbot, accessible through the Pentagon's GenAI.mil portal, has been used by 1.2 million Defense Department employees for unclassified work since December, with personnel running 40 million unique prompts and uploading more than 4 million documents. Training has reportedly not kept pace with adoption, however, as only 26,000 people have completed AI training since December, but future sessions are fully booked, something that suggests more employees are getting on board.
The expansion comes as the Pentagon rapidly broadens its AI partnerships after its standoff with Anthropic, which refused to remove guardrails against domestic surveillance and autonomous weapons from its technology. The Pentagon has since classified the American AI company as a "supply chain risk," which Anthropic will fight in court. Roughly 900 Google and 100 OpenAI employees have since signed an open letter urging their employers to hold firm on the same guardrails. Google quietly altered its "AI Principles" regarding these exact uses in early February.
The Department of Defense has since struck deals with OpenAI and xAI for restricted networks. Google itself faced internal backlash over Pentagon work in 2018 when thousands of employees protested Project Maven, a program that used AI to analyze drone video feeds. It did not renew that contract but has since loosened its restrictions on military work.
This article originally appeared on Engadget at https://www.engadget.com/ai/google-to-provide-pentagon-with-gemini-powered-ai-agents-161037444.html?src=rss
X has told UK’s MPs or Members of Parliament that it suspended 800 million accounts to combat state-backed campaigns on the website, according to The Guardian. Wifredo Fernández, X’s head of global government affairs, told the officials that the suspensions happened over a 12-month period in 2024 and that the accounts were suspended for violating X’s rules on platform manipulation and spam. Russia was allegedly behind most of the accounts that were flooding the website with spam, followed by state actors from China and Iran.
The Russian accounts were trying to “stoke division” and disseminate a “particular type of narrative” to manipulate the 2024 US Presidential Elections, he told MPs on the foreign affairs committee during a video call. Fernández also claimed that the attempts to manipulate discussions and spam on the service aren’t done yet. “There are efforts every single day to create inauthentic networks of accounts,” he said. Apparently, X suspended an additional “several hundred million accounts” last year as well, presumably also due to foreign state-backed manipulation campaigns.
To note, Statista estimates the number of users on X to be 429 million in early 2024. The Guardian also says the platform has approximately 300 million monthly users worldwide.
This article originally appeared on Engadget at https://www.engadget.com/apps/x-says-it-suspended-800-million-accounts-in-2024-over-spam-and-manipulation-123000201.html?src=rss
TikTok doesn’t have to close its offices in Canada after all. The country will allow TikTok to keep its business operational after a national security review, Minister of Industry Mélanie Joly has announced. This is a complete 180 of the country’s decision back in 2024 to order TikTok to shut down its operations, citing unspecified “national security risks” posed by the company and its China-based parent ByteDance. Canadian authorities said back then that their decision was based on evidence collected by the country’s security and intelligence community.
As Bloombergnotes, the order was paused shortly after Mark Carney replaced Justin Trudeau as Prime Minister in early 2025. Carney was the first Canadian PM to visit China in years and had a discussion with President Xi Jinping about tariffs. Joly said TikTok will be allowed to operate in Canada with new enhancements in data security and regulatory oversight. To start with, it will have to implement privacy-enhancing technologies to reduce the risk of unauthorized access that compromise Canadians’ personal information. It will also have to add enhanced protections for minors and ensure transparency by letting an independent third party “audit and continuously verify data access controls.”
“…this decision will protect Canadian jobs, ensuring that TikTok Canada maintains a physical presence in Canada, with commitments to invest in its cultural sector,” Joly said in a statement. “TikTok Canada will support the growth of Canadian creators, artists and cultural organizations, while strengthening the production and accessibility of Canadian cultural content in both official and Indigenous languages across the country.”
This article originally appeared on Engadget at https://www.engadget.com/apps/tiktok-can-continue-its-operations-in-canada-after-agreeing-to-enhanced-security-measures-095239399.html?src=rss
The Netherlands’ military intelligence service and domestic intelligence agency have issued a join warning claiming that Russian hackers have launched "a large-scale global cyber campaign to gain access to Signal and WhatsApp accounts belonging to dignitaries, military personnel and civil servants." According to the Dutch alert, hackers are imitating support chatbots to trick key targets into revealing their PINs for those communication platforms, which allows the bad actors to access incoming messages.
Last year in the US, the Pentagon advised members not to use Signal after the platform was subjected to similar phishing scams by Russian hackers. (Although the same US military leaders proved capable of creating their own security breaches without foreign interference just days prior.)
Having another national government raise concerns about Signal and WhatsApp phishing scams offers yet another reminder to never provide security details or click links without a check on who is really asking for your info.
This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/dutch-intelligence-services-warn-of-russian-hackers-targeting-signal-and-whatsapp-203707202.html?src=rss
Anthropic has filed a lawsuit to prevent the Pentagon from adding the company it a national security blocklist. This comes days after the Department of Defense sent a letter to Anthropic confirming the company was labeled a supply chain risk; at the time CEO Dario Amodei had all but guaranteed Anthropic would fight back with legal action.
The lawsuit claims the designation is unlawful and violated free speech and due process rights. “These actions are unprecedented and unlawful. The Constitution does not allow the government to wield its enormous power to punish a company for its protected speech," Anthropic said in a statement published by Reuters.
Engadget received the following statement from an Anthropic spokesperson:
“Seeking judicial review does not change our longstanding commitment to harnessing AI to protect our national security, but this is a necessary step to protect our business, our customers, and our partners. We will continue to pursue every path toward resolution, including dialogue with the government.”
The lawsuit characterizes the government’s actions as an “unprecedented and unlawful [...] campaign of retaliation.” It goes on to say that “the Constitution does not allow the government to wield its enormous power to punish a company for its protected speech. No federal statute authorizes the actions taken here."
Today’s legal action comes after several weeks of back-and-forth between the AI company and the government. In late February, news broke that the Department of Defense and Defense Secretary Pete Hegseth were pressuring Anthropic to remove certain safeguards from its AI systems, but Amodei made it clear the company would refuse to allow its model to be used for mass surveillance or development of autonomous weapons.
On the February 27 deadline, Amodei refused to budge, leading Hegseth to threaten the company with the supply chain risk designation; he also said the US government would cancel its $200 million contract with the company. The same day, President Trump ordered all federal agencies to cease using Anthropic as well. Despite all this, according to the lawsuit, Anthropic had agreed to “collaborate with the Department on an orderly transition to another AI provider willing to meet its demands.”
Anthropic rival OpenAI stepped into this chaos and quickly made a deal with the Department of Defense. At the time, OpenAI CEO Sam Altman said that two of OpenAI’s most important safety principles are “prohibitions on domestic mass surveillance and human responsibility for the use of force, including for autonomous weapon systems” — the same issues that got Anthropic in hot water. OpenAI then doubled down on the surveillance issue, writing into its contract that “the AI system shall not be intentionally used for domestic surveillance of U.S. persons and nationals.”
Depsite this, OpenAI’s head of robotics hardware resigned from the company this weekend in response to the Defense Department deal. Caitlin Kalinowski wrote on X that “surveillance of Americans without judicial oversight and lethal autonomy without human authorization are lines that deserved more deliberation than they got.”
This article originally appeared on Engadget at https://www.engadget.com/ai/anthropic-sues-us-government-over-supply-chain-risk-designation-152838128.html?src=rss
Following in the footsteps of Australia, Indonesia will be the latest country to limit social media usage for children under 16. Meutya Hafid, Indonesia's communication and digital affairs minister, announced that a new government regulation will require "high-risk" platforms to delete any accounts from Indonesia that are under 16, starting on March 28.
Hafid said in the announcement that the implementation would be done in stages, starting with major platforms like YouTube, TikTok, Facebook, Instagram, Threads, X, Roblox and Bigo Live, a live-streaming platform based in Singapore. The minister added that all platforms will have to fulfill compliance obligations from the Indonesian government, but didn't specify what they were. In response to the ban, a Meta spokesperson told The New York Times that the company hasn't received an official regulation from the country yet and was awaiting details.
While Australia was the first country to implement such a sweeping ban on social media, many other countries are currently in the process of doing the same. Spain's Prime Minister Pedro Sanchez announced last month that the country is also ready to ban social media for users under 16, while Malaysia's cabinet approved a similar ban that will reportedly go into effect sometime this year.
This article originally appeared on Engadget at https://www.engadget.com/social-media/indonesia-announces-a-social-media-ban-for-anyone-under-16-174634956.html?src=rss
FILE PHOTO: Instagram, TikTok, Snapchat, YouTube, Facebook, Twitch and Reddit applications are displayed on a mobile phone ahead of new law banning social media for users under 16 in Australia, in this picture illustration taken on December 9, 2025. REUTERS/Hollie Adams/Illustration//File Photo
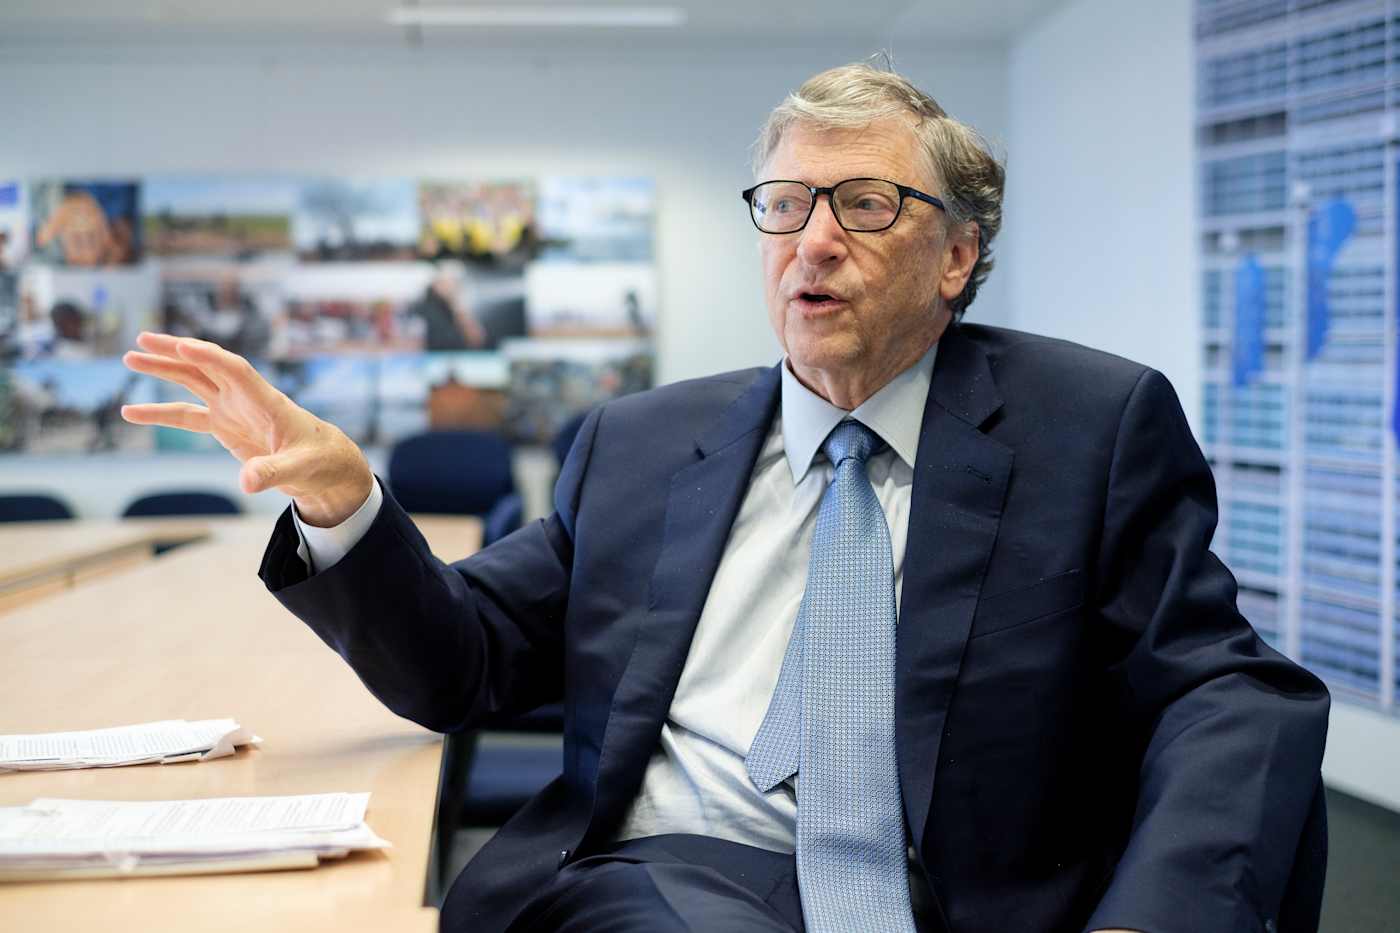
The Nuclear Regulatory Commission has granted approval to TerraPower to begin construction of a reactor in Wyoming. The project is the first new US commercial nuclear reactor in about a decade, according to The New York Times. TerraPower was founded by Bill Gates, and it took years for the business to receive regulatory approval for this construction effort.
TerraPower is part of a push to create more efficient and less expensive nuclear facilities as an alternative power source, particularly as AI companies and data center construction places more demands on the US' current infrastructure. TerraPower's project involves tech it has dubbed Natrium in its planned reactor. Using this liquid sodium approach rather than a traditional light-water reactor is part of how the company aims to reduce costs and time frames.
Advocates see nuclear reactors as a way to generate power without the climate impact of coal or gas plants. Critics point to the safety risks as a severe downside to this approach, while others question whether the creation and disposal of nuclear waste counter the environmental gains. The Gates-backed operation still isn't coming in cheap. The proposed facility could cost at least $4 billion and still faces logistical challenges before coming online as planned in 2031.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/bill-gates-backed-terrapower-begins-nuclear-reactor-construction-221132639.html?src=rss
OpenAI’s Sam Altman said the company will amend its deal with the Defense Department (or the Department of War) to explicitly prohibit the use of its AI system on mass surveillance against Americans. Altman has published an internal memo previously sent to employees on X, telling them that the company will tweak the agreement to add language to make that point especially clear. Specifically, it says:
“Consistent with applicable laws, including the Fourth Amendment to the United States Constitution, National Security Act of 1947, FISA Act of 1978, the AI system shall not be intentionally used for domestic surveillance of U.S. persons and nationals.
For the avoidance of doubt, the Department understands this limitation to prohibit deliberate tracking, surveillance, or monitoring of U.S. persons or nationals, including through the procurement or use of commercially acquired personal or identifiable information.”
Altman has also claimed in the memo that the agency affirmed that its services will not be used by its intelligence agencies, including the NSA, without a modification to their contract. He added that if he received what he believed was an unconstitutional order, he would rather go to jail than follow it.
In addition, the OpenAI CEO has admitted in the memo that the company shouldn’t have rushed to get the deal out on Friday, February 27, since the issues were “super complex and demand clear communication.” Altman explained that the company was “trying to de-escalate things and avoid a much worse outcome” but it “looked opportunistic” in the end. If you’ll recall, OpenAI announced the partnership shortly after President Trump ordered all US government agencies to stop using Claude and any other Anthropic services. To note, Anthropic started working with the US government in 2024.
The Defense Department and Secretary Pete Hegseth had been pressuring Anthropic with to remove its AI’s guardrails so that it can be used for all “lawful” purposes. Those include mass surveillance and the development of fully autonomous weapons. Anthropic refused to bow down to Hegseth’s demands and in a statement said that “no amount of intimidation or punishment” will change its “position on mass domestic surveillance or fully autonomous weapons.” Trump issued the order as a result. The Defense Department had also taken the first steps to designate Anthropic as a “supply chain risk,” which is typically reserved for Chinese companies believed to be working with their country’s government.
Altman said that in his conversations with US officials, he reiterated that Anthropic shouldn’t be designated as a supply chain risk and that he hoped the Defense Department would offer it the same deal OpenAI agreed to. In an AMA session on X over the weekend, Altman clarified that he didn’t know the details of Anthropic’s agreement and how it differed from the one OpenAI signed. But if it had been the same, he thought Anthropic should have agreed to it.
After the news broke out about OpenAI’s deal, Anthropic climbed its way to the number one spot of the App Store's Top Free Apps leaderboard, beating out both ChatGPT and Google Gemini. Anthropic, capitalizing on Claude’s sudden popularity, launched a memory import tool to make switching to its chatbot from another company’s easier. Meanwhile, uninstalls for ChatGPT’s jumped by 295 percent day-over-day, according to Sensor Tower.
Here is re-post of an internal post:
We have been working with the DoW to make some additions in our agreement to make our principles very clear.
1. We are going to amend our deal to add this language, in addition to everything else:
This article originally appeared on Engadget at https://www.engadget.com/ai/openai-will-amend-defense-department-deal-to-prevent-mass-surveillance-in-the-us-050637400.html?src=rss
In a lengthy post on Truth Social on February 27, President Trump ordered all federal agencies to "immediately cease all use of Anthropic's technology" following strong disagreements between the Department of Defense and the AI company. A few hours later, the US conducted a major air attack on Iran with the help of Anthropic's AI tools, according to a report from The Wall Street Journal.
The president noted in his post that there would be a "six-month phase-out period for agencies like the Department of War who are using Anthropic’s products," so federal agencies are still expected to eventually move away from using Claude or other Anthropic tech. It's also not the first time that the US used Anthropic's AI for a major military operation, as the WSJpreviously reported that Claude was used in the capture of the now-removed Venezuelan president Nicolás Maduro.
Moving forward, the Department of Defense may begin transitioning towards other AI options, especially after reaching deals with both xAI and OpenAI to use their models within the federal agency's network. However, the WSJ reported that it would take months to replace Anthropic's Claude with other AI models.
This article originally appeared on Engadget at https://www.engadget.com/ai/the-us-reportedly-used-anthropics-ai-for-its-attack-on-iran-just-after-banning-it-172908929.html?src=rss
OpenAI has reached an agreement with the Defense Department to deploy its models in the agency’s network, company chief Sam Altman has revealed on X. In his post, he said two of OpenAI’s most important safety principles are “prohibitions on domestic mass surveillance and human responsibility for the use of force, including for autonomous weapon systems.” Altman claimed the company put those principles in its agreement with the agency, which he called by the government’s preferred name of Department of War (DoW), and that it had agreed to honor them.
The agency has closed the deal with OpenAI, shortly after President Donald Trump ordered all government agencies to stop using Claude and any other Anthropic services. If you’ll recall, US Defense Secretary Pete Hegseth previously threatened to label Anthropic “supply chain risk” if it continues refusing to remove the guardrails on its AI, which are preventing the technology to be used for mass surveillance against Americans and in fully autonomous weapons.
It’s unclear why the government agreed to team up with OpenAI if its models also have the same guardrails, but Altman said it’s asking the government to offer the same terms to all the AI companies it works with. Jeremy Lewin, the Senior Official Under Secretary for Foreign Assistance, Humanitarian Affairs, and Religious Freedom, said on X that DoW “references certain existing legal authorities and includes certain mutually agreed upon safety mechanisms” in its contracts. Both OpenAI and xAI, which had also previously signed a deal to deploy Grok in the DoW’s classified systems, agreed to those terms. He said it was the same “compromise that Anthropic was offered, and rejected.”
Anthropic, which started working with the US government in 2024, refused to bow down to Hegseth. In its latest statement, published just hours before Altman announced OpenAI’s agreement, it repeated its stance. “No amount of intimidation or punishment from the Department of War will change our position on mass domestic surveillance or fully autonomous weapons,” Anthropic wrote. “We will challenge any supply chain risk designation in court.”
Altman added in his post on X that OpenAI will build technical safeguards to ensure the company’s models behave as they should, claiming that’s also what the DoW wanted. It’s sending engineers to work with the agency to “ensure [its models’] safety,” and it will only deploy on cloud networks. As The New York Timesnotes, OpenAI is not yet on Amazon cloud, which the government uses. But that could change soon, as company has also just announced forming a partnership with Amazon to run its models on Amazon Web Services (AWS) for enterprise customers.
Tonight, we reached an agreement with the Department of War to deploy our models in their classified network.
In all of our interactions, the DoW displayed a deep respect for safety and a desire to partner to achieve the best possible outcome.
This article originally appeared on Engadget at https://www.engadget.com/ai/openai-strikes-a-deal-with-the-defense-department-to-deploy-its-ai-models-054441785.html?src=rss
President Donald Trump has ordered all US government agencies to stop using Claude and other Anthropic services, escalating an already volatile feud between the Department of Defense and company over AI safeguards. Taking to Truth Social on Friday afternoon, the president said there would be a six-month phase out period for federal agencies, including the Defense Department, to migrate off of Anthropic's products.
“The Leftwing nut jobs at Anthropic have made a DISASTROUS MISTAKE trying to STRONG-ARM the Department of War, and force them to obey their Terms of Service instead of our Constitution,” the president wrote. “Anthropic better get their act together, and be helpful during this phase out period, or I will use the Full Power of the Presidency to make them comply, with major civil and criminal consequences to follow.”
Before today, US Defense Secretary Pete Hegseth had threatened to label Anthropic a “supply chain risk” if it did not agree to withdraw safeguards that insist Claude not be used for mass surveillance against Americans or in fully autonomous weapons. In a post on X published after President Trump’s statement, Hegseth said he was “directing the Department of War to designate Anthropic a Supply-Chain Risk to National Security. Effective immediately, no contractor, supplier, or partner that does business with the United States military may conduct any commercial activity with Anthropic.”
Anthropic did not immediately respond to Engadget's comment request. Earlier in the day, a spokesperson for the company said the contract Anthropic received after CEO Dario Amodei outlined Anthropic's position made “virtually no progress” on preventing the outlined misuses.
"New language framed as a compromise was paired with legalese that would allow those safeguards to be disregarded at will. Despite DOW's recent public statements, these narrow safeguards have been the crux of our negotiations for months," the spokesperson said. "We remain ready to continue talks and committed to operational continuity for the Department and America's warfighters."
Advocacy groups like the Center for Democracy and Technology (CDT) quickly came out against the president’s threats. “This action sets a dangerous precedent. It chills private companies’ ability to engage frankly with the government about appropriate uses of their technology, which is especially important in national security settings that so often have reduced public visibility,” said CDT President and CEO Alexandra Givens, in a statement shared with Engadget. “These threats undermine the integrity of the innovation ecosystem, distort market incentives and normalize an expansive view of executive power that should worry Americans all across the political spectrum.”
For now, it appears the AI industry is united behind Anthropic. On Friday, hundreds of Google and OpenAI employees signed an open letter urging their companies to stand in "solidarity" with the lab. According to an internal memo seen by Axios, OpenAI CEO Sam Altman said the ChatGPT maker would draw the same red line as Anthropic.
In a blog post published late on Friday, Anthropic vowed to “challenge any supply chain risk designation in court,” and assured its customers that only work related to the Defense Department would be affected. The company's full statement is available here, an excerpt is below:
Designating Anthropic as a supply chain risk would be an unprecedented action—one historically reserved for US adversaries, never before publicly applied to an American company. We are deeply saddened by these developments. As the first frontier AI company to deploy models in the US government’s classified networks, Anthropic has supported American warfighters since June 2024 and has every intention of continuing to do so.
We believe this designation would both be legally unsound and set a dangerous precedent for any American company that negotiates with the government.
No amount of intimidation or punishment from the Department of War will change our position on mass domestic surveillance or fully autonomous weapons. We will challenge any supply chain risk designation in court.
Update, February 27, 9PM ET: This story was updated twice after publish. First at 6PM ET to include a link to and quotes from Hegseth about the designation of Anthropic as a supply chain risk. Later, a quote from Anthropic was added, along with a link to the company’s blog post on the subject.
This article originally appeared on Engadget at https://www.engadget.com/ai/trump-orders-federal-agencies-to-drop-anthropic-services-amid-pentagon-feud-222029306.html?src=rss
Despite an ultimatum from Defense Secretary Pete Hegseth, Anthropic said that it can't "in good conscience" comply with a Pentagon edict to remove guardrails on its AI, CEO Dario Amodei wrote in a blog post. The Department of Defense had threatened to cancel a $200 million contract and label Anthropic a "supply chain risk" if it didn't agree to remove safeguards over mass surveillance and autonomous weapons.
"Our strong preference is to continue to serve the Department and our warfighters — with our two requested safeguards in place," Amodei said. "We remain ready to continue our work to support the national security of the United States."
In response, US Under Secretary of Defense Emil Michael accused Amodei in a post on X of wanting "nothing more than to try to personally control the US military and is OK putting our nation's safety at risk."
The standoff began when the Pentagon demanded that Anthropic its Claude AI product available for "all lawful purposes" — including mass surveillance and the development of fully autonomous weapons that can kill without human supervision. Anthropic refused to offer its tech for those things, even with a "safety stack" built into that model.
Yesterday, Axios reported that Hegseth gave Anthropic a deadline of 5:01 PM on Friday to agree to the Pentagon's terms. At the same time, the DoD requested an assessment of its reliance on Claude, an initial step toward potentially labelling Anthropic as a "supply chain risk" — a designation usually reserved for firms from adversaries like China and "never before applied to an American company," Anthropic wrote.
Amodei declined to change his stance and stated that if the Pentagon chose to offboard Anthropic, "we will work to enable a smooth transition to another provider, avoiding any disruption to ongoing military planning, operations or other critical missions." Grok is one of the other providers the DoD is reportedly considering, along with Google's Gemini and OpenAI.
It may not be that simple for the military to disentangle itself from Claude, however. Up until now, Anthropic's model has been the only one allowed for the military's most sensitive tasks in intelligence, weapons development and battlefield operations. Claude was reportedly used in the Venezuelan raid in which the US military exfiltrated the country's president, Nicolás Maduro, and his wife.
AI companies have been widely criticized for potential harm to users, but mass surveillance and weapons development would clearly take that to a new level. Anthropic's potential reply to the Pentagon was seen as a test of its claim to be the most safety-forward AI company, particularly after dropping its flagship safety pledge a few days ago. Now that Amodei has responded, the focus will shift to the Pentagon to see if it follows through on its threats, which could seriously harm Anthropic.
This article originally appeared on Engadget at https://www.engadget.com/ai/anthropic-refuses-to-bow-to-pentagon-despite-hegseths-threats-085553126.html?src=rss
The Anthropic AI logo is displayed on a mobile phone screen in this photo illustration in Brussels, Belgium, on February 24, 2026. (Photo by Jonathan Raa/NurPhoto via Getty Images)
Canadian officials summoned leaders from OpenAI to Ottawa this week to address safety concerns about ChatGPT. The crux of the government concerns was that OpenAI did not notify authorities when it banned the account of a user who allegedly committed a mass shooting in British Columbia earlier this month.
"The message that we delivered, in no uncertain terms, was that we have an expectation that there are going to be changes implemented, and if they're not forthcoming very quickly, the government is going to be making changes," Justice Minister Sean Fraser said of the company and its AI chatbot. It's unclear what those government-led changes or rules might be. There have been two previous, unsuccessful attempts to pass an online harms act in Canada.
A recent report by The Wall Street Journal claimed that in 2025, some OpenAI employees flagged the account of the alleged shooter, Jesse Van Rootselaar, as containing potential warnings of committing real-world violence and called for leadership to notify law enforcement. Although Van Rootselaar's account was banned for policy violations, a company rep said that the account activity did not meet OpenAI's criteria for engaging the local police.
“Those reports were deeply disturbing, reports saying that OpenAI did not contact law enforcement in a timely manner," said Canadian Artificial Intelligence Minister Evan Solomon ahead of the discussion with company leaders. "We will have a sit-down meeting to have an explanation of their safety protocols and when they escalate and their thresholds of escalation to police, so we have a better understanding of what’s happening and what they do."
OpenAI has been implicated in mulitple wrongful death suits. The company's ChatGPT was accused of encouraging "paranoid beliefs" before a man killed his mother and himself in a December 2025 lawsuit. It is also at the center of one of several wrongful death lawsuits against the makers of AI chatbots for helping teenagers plan and commit suicides.
This article originally appeared on Engadget at https://www.engadget.com/ai/canadian-government-demands-safety-changes-from-openai-204924604.html?src=rss
 Anmelden