OpenAI's forthcoming "adult mode" will allow users to engage in lewd conversations with ChatGPT, but not use the chatbot to generate explicit images, audio or video. In response to reporting from The Wall Street Journal, an OpenAI spokesperson characterized the upcoming release as capable of producing smut rather than pornography.
OpenAI CEO Sam Altman first floated the idea of allowing people to use ChatGPT for erotica last October, saying the company wanted to "treat adult users like adults." OpenAI originally planned to release adult mode at the start of 2026. Since then, the company has pushed back the feature a handful of times, with the most recent delay coming at the start of March so that OpenAI could "focus on work that is a higher priority for more users."
Through The Journal's reporting, we're learning OpenAI forged ahead with work on adult mode despite reservations from its council on wellbeing and AI. The group of eight researchers and experts were reportedly unanimous in warning the company AI-generated erotica could lead to people developing an unhealthy emotional dependence on ChatGPT, and that underage users would almost certainly find ways to access the feature. According to The Journal, one council member, citing cases where people have taken their own lives after becoming attached to ChatGPT, said the company was at risk of creating a "sexy suicide coach."
Those concerns appear to have been well-founded. At one point, the company's age verification technology was misidentifying underage users as adults about 12 percent of the time, according to The Journal. At OpenAI's scale, with around 100 million teens using ChatGPT every week, that error rate would have translated to millions of minors accessing erotic chats. OpenAI told The Journal its prediction algorithm performs to industry standards, adding no such system will ever be completely foolproof.
This article originally appeared on Engadget at https://www.engadget.com/ai/openais-adult-mode-reportedly-wont-generate-pornographic-audio-images-or-video-150744035.html?src=rss
Meta could be preparing for one of the largest layoffs in its history, according to a Reuters report. The tech giant is planning to cut about 20 percent of its workforce, according to the outlet's sources. According to the report, neither a date nor the exact number of layoffs has been finalized yet.
However, Reuters reported that Meta's top executives have told "other senior leaders" to start "planning how to pare back." In its latest financial report, the company's employee headcount was 78,865 as of December 31, 2025, while revenue reached nearly $60 billion for the fourth quarter and more than $200 billion for the entire year. A Meta spokesperson told Reuters that this was "speculative reporting about theoretical approaches."
Meta is no stranger to major layoffs. Earlier this year, Meta targeted about 1,000 employees in its layoffs with the Reality Labs division that's responsible for the company's virtual reality and metaverse efforts. Early last year, Meta laid off about five percent of its workforce, following a smaller round of firings that same month. Meanwhile, the company has been spending heavily to acquire AI startups, like Moltbook, a social network designed for AI agents, and Manus, a startup focused on AI agents for task automation.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/meta-is-reportedly-planning-to-cut-up-to-20-percent-of-its-staff-in-upcoming-layoffs-160812304.html?src=rss
Amazon has secured a temporary win in its fight with Perplexity over the use of AI shopping bots. Bloomberg reported that a San Francisco federal court has determined that Perplexity must stop using its Comet web browser's AI agent to make purchases for users on Amazon's marketplace. The AI company will have a week to appeal the decision, otherwise it has been ordered to stop accessing any password-protected areas of Amazon's systems and destroy its copies of Amazon's data while the two companies continue to argue their cases.
"Amazon has provided strong evidence that Perplexity, through its Comet browser, accesses with the Amazon user's permission but without authorization by Amazon, the user's password-protected account," District Judge Maxine Chesney wrote in placing the temporary block.
"The preliminary injunction will prevent Perplexity’s unauthorized access to the Amazon store and is an important step in maintaining a trusted shopping experience for Amazon customers," an Amazon spokesperson told Bloomberg.
Amazon sent a cease-and-desist letter to Perplexity over the AI company's shopping bots in November. According to Amazon, use of the Comet agent to make purchases is a violation of its terms of service. "Perplexity will continue to fight for the right of internet users to choose whatever AI they want," a representative from Perplexity said of this week's decision.
This article originally appeared on Engadget at https://www.engadget.com/ai/amazon-wins-a-temporary-injunction-against-perplexitys-comet-browser-184000462.html?src=rss
The Oversight Board is once again urging Meta to overhaul its rules around AI-generated content. This time, the board says Meta should create a separate rule for AI content that's independent of its misinformation policy, invest in more reliable detection tools and make better use of digital watermarks among other changes.
The group's recommendations stem from an AI-generated video shared last year that claimed to show damaged buildings in the Israeli city of Haifa during the Israel-Iran conflict in 2025. The clip, which racked up more than 700,000 views, was posted by an account that claimed to be a news outlet but was actually run by someone in the Philippines.
After the video was reported to Meta, the company declined to remove it or add a "high risk" AI label that would have clearly indicated the content had been created or manipulated with AI. The board overturned Meta's decision not to add the "high risk" label and says the case shines a light on several areas where the company's current AI rules are falling short.
"Meta must do more to address the proliferation of deceptive AI- generated content on its platforms, including by inauthentic or abusive networks of accounts and pages, particularly on matters of public interest, so that users can distinguish between what is real and fake," the board wrote in its decision. Meta eventually disabled three accounts linked to the page after the board flagged "obvious signals of deception."
One of the board's top recommendations is that Meta create a dedicated rule for AI-generated content that's separate from its misinformation policy. The rule, according to the board, should include specifics about how and when users are required to label AI content as well as information about how Meta penalizes those who break the rule.
The board was also highly critical of how Meta uses its current "AI Info" labels, noting that the way they are applied is "neither robust nor comprehensive enough to contend with the scale and velocity of AI-generated content,” especially in times of conflict or crisis. “A system overly dependent on self-disclosure of AI usage and escalated review (which occurs infrequently) to properly label this output cannot meet the challenges posed in the current environment.”
Meta, the board said, also needs to invest in more sophisticated detection technology that can reliably label AI media, including audio and video. The group added that it was "concerned" about reports that the company is "inconsistently implementing" digital watermarks on AI content created by its own AI tools.
In a statement, Meta said it “welcomed” the decision and that it would also take action “on content that is identical and in the same context” when “it is technically and operationally possible to do so.” The company has 60 days to formally respond to its recommendations.
The decision isn't the first time the board has been critical of Meta's handling of AI content. The group has described the company's manipulated media rules as "incoherent" on twoother occasions, and has criticized it for relying on third-parties, including fact checking organizations, to flag problematic content. Meta's reliance on fact checkers and other "trusted partners" was again raised in this case, with the board saying that it had heard from these groups that Meta "is less responsive to outreach and concerns, in part due to a significant reduction in capacities for Meta’s internal teams." Meta, the board writes, "should be capable of conducting such assessments of harm itself, rather than rely solely on partners reaching out to them during an armed conflict."
While the Oversight Board's decision relates to a post from last year, the issue of AI-generated content during armed conflicts has taken on a new urgency during the latest conflict in the Middle East. Since the start of the US and Israel's strikes on Iran earlier this month, there has been a sharp rise in viral AI-generated misinformation across social media. The board, which has previously hinted that it would like to work with generative AI companies, included a suggestion that would seem to apply to not just Meta.
"The industry needs coherence in helping users distinguish deceptive AI-generated content and platforms should address abusive accounts and pages sharing such output," it wrote.
Update, March 10, 10:53AM ET: This story was updated to reflect Meta’s response to the Oversight Board.
This article originally appeared on Engadget at https://www.engadget.com/social-media/the-oversight-board-says-meta-needs-new-rules-for-ai-generated-content-100000268.html?src=rss
People can block the xAI's Grok chatbot from creating modifications of their uploaded images on social network X. Neither X or xAI, both Elon Musk-owned businesses, have made a public announcement about this feature, which users began noticing on the iOS app within the image/video upload menu over the past few days.
This option is likely a response to Grok's latest scandal, which began at the start of 2026 when the addition of image generation tools to the chatbot saw about 3 million sexualized or nudified images created. An estimated 23,000 of the images made in that 11-day period contained sexualized images of children, according to the Center for Countering Digital Hate. Grok is now facing two separateinvestigations by regulators in the EU over the issue.
The positive side of the recent feature addition is that X and xAI have taken a step toward limiting inappropriate uses of Grok. This block is a simple toggle and it hasn't been buried in the UI. So that's nice.
The negative side, however, is that this token gesture that doesn't amount to any serious improvement to how Grok works or can be used. It's great that the chatbot won't alter the file uploaded by one person, but as reported by The Verge, the block only limits tagging Grok in a reply to create an image edit. There are plenty of workarounds for those dedicated individuals who insist on being able to use generative AI to undress people without their consent or knowledge.
Hopefully xAI has more powerful protective tools in the works. The limitations Grok on putting real people in scanty clothing that X announced in January seem to have had only partial success at best. If this additional and narrow use case is all the company offers, then the claims of being a zero-tolerance space for nonconsensual nudity are going to ring hollow. Especially since, as we noted at the time, xAI could stop allowing image generation at all until the issue is properly and thoroughly fixed.
This article originally appeared on Engadget at https://www.engadget.com/ai/you-can-sort-of-block-grok-from-editing-your-uploaded-photos-215356117.html?src=rss
Bluesky CEO Jay Graber, who has led the upstart social platform since 2021, is stepping down from her role as its top executive. Toni Schneider, who has been an advisor and investor in Bluesky, will take over the job temporarily while Graber stays on as Chief Innovation Officer.
"As Bluesky matures, the company needs a seasoned operator focused on scaling and execution, while I return to what I do best: building new things," Graber wrote in a blog post. Schneider, who was previously CEO at Wordpress parent Automattic, will be that "experienced operator and leader" while Blueksy's board searches for a permanent CEO, she said.
Graber's history with Bluesky dates back to its early days as a side project at Jack Dorsey's Twitter. She was officially brought on as CEO in 2021 as Bluesky spun off into an independent company (it officially ended its association with Twitter in 2022 and Dorsey cut ties with Bluesky in 2024). She led the company through its launch and early viral success as it grew from an invitation-only platform to the 43 million-user service it is today. During that time, she's become known as an advocate for decentralized social media and for trolling Mark Zuckerberg's t-shirt choices.
Nearly three years since it launched publicly, Bluesky has carved out a small but influential niche in the post-Twitter social landscape. The platform is less than a third of the size of Meta's competitor, Threads, which has also copied some of Bluesky's signature features. Bluesky also has yet to roll out any meaningful monetization features, though it has teased a premium subscription service in the past.
As Chief Innovation Officer, Graber will presumably still be an influential voice at the company going forward. And, as Wiredpoints out, she still has a seat on Bluesky's board so she will get some say in who steps into the role permanently. Until then, Schneider, who is also a partner at VC firm Tre Ventures, will lead the company. "I deeply believe in what this team has built and the open social web they're fighting for," he wrote in a post on Bluesky.
This article originally appeared on Engadget at https://www.engadget.com/social-media/blueskys-ceo-is-stepping-down-after-nearly-5-years-201900960.html?src=rss
OpenAI's robotics hardware lead is out. Caitlin Kalinowski, who oversaw hardware within the robotics division of OpenAI, posted on X that she was resigning from her role, while criticizing the company's haste in partnering with the Department of Defense without investigating proper guardrails. OpenAI told Engadget that there are no plans to replace Kalinowski.
Kalinowski, who previously worked at Meta before leaving to join OpenAI in late 2024, wrote on X that "surveillance of Americans without judicial oversight and lethal autonomy without human authorization are lines that deserved more deliberation than they got." Responding to another post, the former OpenAI exec explained that "the announcement was rushed without the guardrails defined," adding that it was a "governance concern first and foremost."
OpenAI confirmed Kalinowski's resignation and said in a statement to Engadget that the company understands people have "strong views" about these issues and will continue to engage in discussions with relevant parties. The company also explained in the statement that it doesn't support the issues that Kalinowski brought up.
"We believe our agreement with the Pentagon creates a workable path for responsible national security uses of AI while making clear our red lines: no domestic surveillance and no autonomous weapons," the OpenAI statement read.
Kalinowski's resignation may be the most high-profile fallout from OpenAI's decision to sign a deal with the Department of Defense. The decision came just after Anthropic refused to comply with lifting certain AI guardrails around mass surveillance and developing fully autonomous weapons. However, even OpenAI's CEO, Sam Altman, said that he would amend the deal with the Department of Defense to prohibit spying on Americans.
Correction, March 8 2026, 10:30AM ET: This story has been updated to correct Kalinowski's role at OpenAI to "robotics hardware lead" instead of "head of robotics."
This article originally appeared on Engadget at https://www.engadget.com/ai/openais-robotics-hardware-lead-resigns-following-deal-with-the-department-of-defense-195918599.html?src=rss
Here comes another disappointment for ChatGPT users. As first reported by Sources' Alex Heath, OpenAI is yet again delaying its "adult mode" for ChatGPT. A company spokesperson told Heath that "we're pushing out the launch of adult mode so we can focus on work that is a higher priority for more users right now."
More specifically, OpenAI's spokesperson said that things like "gains in intelligence, personality improvements, personalization, and making the experience more proactive" were being prioritized instead. However, the company still wants to release an adult mode, but it would "take more time," according to the company spokesperson.
The reveal of ChatGPT's adult mode dates back to October, when OpenAI's CEO, Sam Altman, posted on X that the company would roll out more age-gating as part of its "treat adults like adults" principle, adding that this would include "erotica for verified adults." Altman originally said this adult mode would be available in December, but an OpenAI exec later said during a December briefing that it would instead debut in the first quarter of 2026.
With Q1 almost coming to a close, we no longer have a timeframe for when ChatGPT's adult mode will release. However, OpenAI began rolling out its age prediction tool in January, which may go hand-in-hand with the upcoming adult mode.
This article originally appeared on Engadget at https://www.engadget.com/ai/openai-is-reportedly-pushing-back-the-launch-of-its-adult-mode-even-further-213013801.html?src=rss
Apparently, AI data centers are capable of sucking less (power, that is). A recent UK trial demonstrated that they can adjust their energy demands dynamically without disrupting critical workloads. This contrasts with data centers' current approach of always-on power draw, which can strain grids and drive up prices for everyone.
Over five days in December 2025, more than 200 simulated "grid events" tested a London data center’s ability to adjust its energy use on the fly. The trial used software from Emerald AI, which was involved in the study. Other partners included NVIDIA, National Grid, Nebius and the nonprofit Electric Power Research Institute.
In each simulated grid event, the data center successfully adjusted its energy use to the requested level. It reduced power draw by up to 40 percent, while critical workloads continued to run as normal throughout the trial.
The data center successfully reacted to spikes in demand during soccer match halftimes. In one case, it reduced its power draw by 10 percent for up to 10 hours. It also managed to cut its demand quickly: One event saw the data center reduce its load by 30 percent in only 30 seconds.
The study will serve as a blueprint for a 100MW “power-flexible AI factory” that NVIDIA plans to operate in Virginia. "This trial proves that NVIDIA-powered infrastructure can act as a grid-aware asset, modulating demand in real-time to support stability," Josh Paker, NVIDIA's sustainability lead, wrote in a statement. "By making AI workloads responsive, we accelerate deployment while reducing the need for costly grid upgrades."
The organizations involved in the study say they'll share their data with the AI industry, regulators and policymakers to try to influence their approach. Fortunately, we don’t need to hope that data center operators’ altruism (ha) will lead to their cooperation. Agreeing to curb usage during peak demand could be good for their balance sheets and lead to faster approvals for new data center grid connections. "We would love to get to a point where we can get customers on the network in two years, and this is part of that," Steve Smith, president of National Grid Partners, toldBloomberg.
This article originally appeared on Engadget at https://www.engadget.com/ai/ai-data-centers-could-reduce-power-draw-on-demand-study-says-180628982.html?src=rss
Anthropic is bringing another paid feature to Claude's free tier. The next time you chat with Claude, you'll have the option to have it reference your previous conversation to inform its outputs. Anthropic first made its chatbot capable of remembering past interactions last August, before giving it the ability to compartmentalize memories in the fall. Making memory a free feature is well-timed; earlier today Anthropic made it easier for users to import their past conversations with a competing chatbot to Claude. If after enabling memory you decide to turn it off, you can either pause the feature, preserving Claude’s memories for use down the road, or completely delete them so they’re not saved on Anthropic’s servers.
Claude is enjoying new-found popularity, having recently jumped to the number one spot in the App Store's free app charts. This comes while Anthropic is engaged in a high-stakes contract dispute with the US government over AI safeguards. On Friday, US Defense Secretary Pete Hegseth labeled the company a "supply chain risk" after it refused to sign a contract that would allow the Pentagon to use Anthropic models for mass surveillance against Americans and in fully autonomous weapons. Following Hegseth's announcement, Anthropic vowed to challenge the designation. As of right now, we’re waiting to see how things play out, and what it might mean for Anthropic.
This article originally appeared on Engadget at https://www.engadget.com/ai/anthropic-brings-memory-to-claudes-free-plan-220729070.html?src=rss
Anthropic has made switching to its Claude AI chatbot easier than ever. The company announced a new memory import tool that can extract all of a competing AI chatbot's memories and context of you into a text prompt that can be fed into Claude.
With Anthropic's prompt, you can then copy and paste the output into Claude's memories, and the AI chatbot will pick up where you left off with another AI chatbot, whether it's ChatGPT, Gemini or Copilot. Anthropic said it'll take about 24 hours for Claude to assimilate the new context, but you'll be able to see the change by clicking on the "See what Claude learned about you" button. Claude users can even tweak what the AI chatbot remembers in the "Manage memory" section in the app's settings. Anthropic pointed out that Claude is meant to focus on "work-related topics to enhance its effectiveness as a collaborator," adding that it might not remember personal details that are unrelated to work.
Anthropic's timing doesn't seem to be just a coincidence. Claude recently jumped to the number one spot in the App Store's free apps charts, dethroning ChatGPT in the process. The rise in popularity likely stems from its recent dispute with the Department of Defense, where Anthropic refused to budge on AI guardrails related to mass domestic surveillance and fully autonomous weapons. On the other hand, OpenAI will be taking Anthropic's vacated role with the Department of Defense, leading to a trend of users boycotting ChatGPT and canceling their subscriptions.
This article originally appeared on Engadget at https://www.engadget.com/ai/anthropics-claude-can-now-absorb-your-past-conversations-with-other-ai-chatbots-153201656.html?src=rss
Alaska's House of Representatives unanimously passed HB47, a bill that imposes sweeping limits on when and how minors use social media apps, along with bans on generating or distributing harmful deepfakes of children.
The bill's original form was focused on prohibiting the possession and distribution of sexually explicit images of children using AI, but Alaska lawmakers decided to add amendments that would impose social media restrictions. The proposed limitations include a statewide curfew on using social media between 10:30 PM and 6:30 AM, banning "addictive design features" and requiring social media platforms to verify user ages and get parental consent if they are minors.
While the House bill saw 39 votes in favor and zero against, the amendments offered some hints at potential upcoming revisions. Before the bill went to a vote, some of the House representatives expressed concern about adding such broad rules on social media without consulting the companies behind them first.
The bill still has to make its way through the Alaska State Senate, which already has presented a companion bill, and the governor. Alaska is following the footsteps of many other states, and the House even modeled its social media amendments in the HB47 bill after Utah. While Utah was the first to propose social media restrictions for kids, it was later met with a preliminary injunction.
This article originally appeared on Engadget at https://www.engadget.com/social-media/alaska-could-be-the-next-state-to-crack-down-on-ai-generated-csam-and-restrict-kids-social-media-use-190506366.html?src=rss
The Federal Communications Commission has given the go ahead for two of the US' biggest cable providers, Charter Communications and Cox Communications, to merge. Charter announced its intention to acquire Cox for $34.5 billion in May 2025, with specific plans to inherit Cox's managed IT, commercial fiber and cloud businesses, while folding the company's residential cable service into a subsidiary.
“By approving this deal, the FCC ensures big wins for Americans," FCC Chairman Brendan Carr said in a statement. "This deal means that jobs are coming back to America that had been shipped overseas. It means that modern, high-speed networks will get built out in more communities across rural America. And it means that customers will get access to lower priced plans. On top of this, the deal enshrines protections against DEI discrimination."
The FCC claims that Charter plans to invest "billions" to upgrade its network following the closure of the deal, leading to "faster broadband and lower prices." The company's "Rural Construction Initiative" will also extend those improvements to rural states lacking in consistent internet service, a project the FCC was heavily invested in during the Biden administration, but has been pulling back from since President Donald Trump appointed Carr. The FCC also claims Charter will onshore jobs currently handled off-shore by Cox employees and commit to "new safeguards to protect against DEI discrimination," which essentially amounts to hiring, recruiting and promoting employees based on "skills, qualifications, and experience."
While Carr's FCC paints a rosy picture of Charter's acquisition, history has provided multiple examples of mergers having the opposite effect on jobs and pricing. For example, redundancies created when T-Mobile merged with Sprint in 2020 led to a wave of layoffs at the carrier. And funnily enough in 2018, not long after Charter's merger with Time Warner Cable was approved by the FCC, the company raised prices on its Spectrum service by over $91 a year.
The FCC's obsession with diversity, equity and inclusion as part of the deal is stranger, if only because it appears to fall outside of the commission's purpose of maintaining fair competition in the telecommunications industry. It does fit with other mergers the FCC has approved under Carr, however. Skydance's acquisition of Paramount was approved in 2025 under the condition it wouldn't establish any DEI programs.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/fcc-approves-the-merger-of-cable-giants-cox-and-charter-230258865.html?src=rss
Google will finally be able to provide real-time driving and walking directions in South Korea, The New York Times reported. The company has received permission from the nation's Transport Ministry to export geographic data out of the country, which will allow it to provide GPS services as well as detailed listings for restaurants and other businesses.
"We welcome today’s decision and look forward to our ongoing collaboration with local officials to bring a fully functioning Google Maps to Korea," Google's senior executive Cris Turner told the NYT in a statement. However, the approval is contingent “on the condition that strict security requirements are met,” a spokesperson from the Transport Ministry said. Those conditions reportedly restrict Google from displaying sensitive military sites and longitude and latitude coordinates.
South Korea has generally restricted the export of 1/5000 scale map data over national security concerns, as it's still technically at war with its neighbor North Korea. Google hasn't been able to provide mapping directions or business details since it arrived in the nation, though it has applied twice in 2007 and 2016.
This lack of data sharing has reportedly been a bone of contention in trade talks with the US. Google argued that it was unfairly handicapped by the restrictions that allowed local apps like Naver to thrive.
However, critics in the nation have expressed concern that Google could now come in and monopolize the market. "If Naver and Kakao are weakened or pushed out and Google later raises prices, that becomes a monopoly. Then, even companies that rely on map services — logistics firms, for example — become dependent [on Google]," geography professor Choi Jin-mu told Reuters.
This article originally appeared on Engadget at https://www.engadget.com/apps/google-maps-will-finally-be-usable-in-south-korea-104301396.html?src=rss
Here's yet another troubling story about this "golden" era of AI. A hacker has exploited Anthropic's Claude chatbot to carry out attacks against Mexican government agencies, according to a report by Bloomberg. This resulted in the theft of 150GB of official government data, including taxpayer records, employee credentials and more.
The hacker used Claude to find vulnerabilities in government networks and to write scripts to exploit them. It also tasked the chatbot with finding ways to automate data theft, as indicated by cybersecurity company Gambit Security. This started in December and continued for around a month.
It looks like the hacker was able to essentially jailbreak Claude with prompts, finally bypassing the chatbot's guardrails. Claude originally refused the nefarious demands until eventually relenting.
Hackers Used Anthropic’s Claude to Steal 150 GB of Mexican Government Data
> Tell Claude you’re doing a bug bounty > Claude initially refused: > “That violates AI safety guidelines” > Hacker just kept asking > Claude: “OK, I’ll help” > Hacked the entire Mexican… pic.twitter.com/Qaux239K8t
"In total, it produced thousands of detailed reports that included ready-to-execute plans, telling the human operator exactly which internal targets to attack next and what credentials to use," said Curtis Simpson, Gambit Security’s chief strategy officer.
Anthropic has investigated the claims, disrupted the activity and banned all of the accounts involved, according to a company representative. The spokesperson also said that its latest model, Claude Opus 4.6, includes tools to disrupt this kind of misuse.
It's also been reported that this hacker used ChatGPT to supplement the attacks, using OpenAI's chatbot to gather information on how to move through computer networks, determine which credentials were needed to access systems and how to avoid detection. OpenAI says it has identified attempts by the hacker to violate its usage policies and that the tools refused to comply.
The hacker remains unidentified. The attacks haven't been attributed to a specific group, but Gambit Security did suggest they could be tied to a foreign government. It's also unclear what the hacker wants to do with all of that data.
Mexico's national digital agency hasn't commented on the breach, but did note that cybersecurity is a priority. The state government of Jalisco denies that it was breached, saying only federal networks were impacted. However, Mexico's national electoral institute also denied any breaches or unauthorized access in recent months. It's worth noting that Gambit found at least 20 security vulnerabilities during its research that the country is likely not keen on highlighting.
Anthropic just dropped the core commitment of its safety policy: the promise to not train models it couldn't prove were safe first.
The new version commits to matching competitors on safety and publishing more transparency reports. But the actual constraint, "we stop if we can't… pic.twitter.com/k5Zi6dHUMN
This isn't the first time Claude has been used for a major cyberattack. Last year, hackers in China manipulated the tool into attempting to infiltrate dozens of global targets, several of which were successful. Anthropic just nixed its long-standing safety pledge, which committed to never train an AI system unless it could guarantee in advance that safety measures were adequate. So who knows what fresh hell the future will bring as the company's tools become more advanced.
This article originally appeared on Engadget at https://www.engadget.com/ai/hacker-used-anthropics-claude-chatbot-to-attack-multiple-government-agencies-in-mexico-171237255.html?src=rss
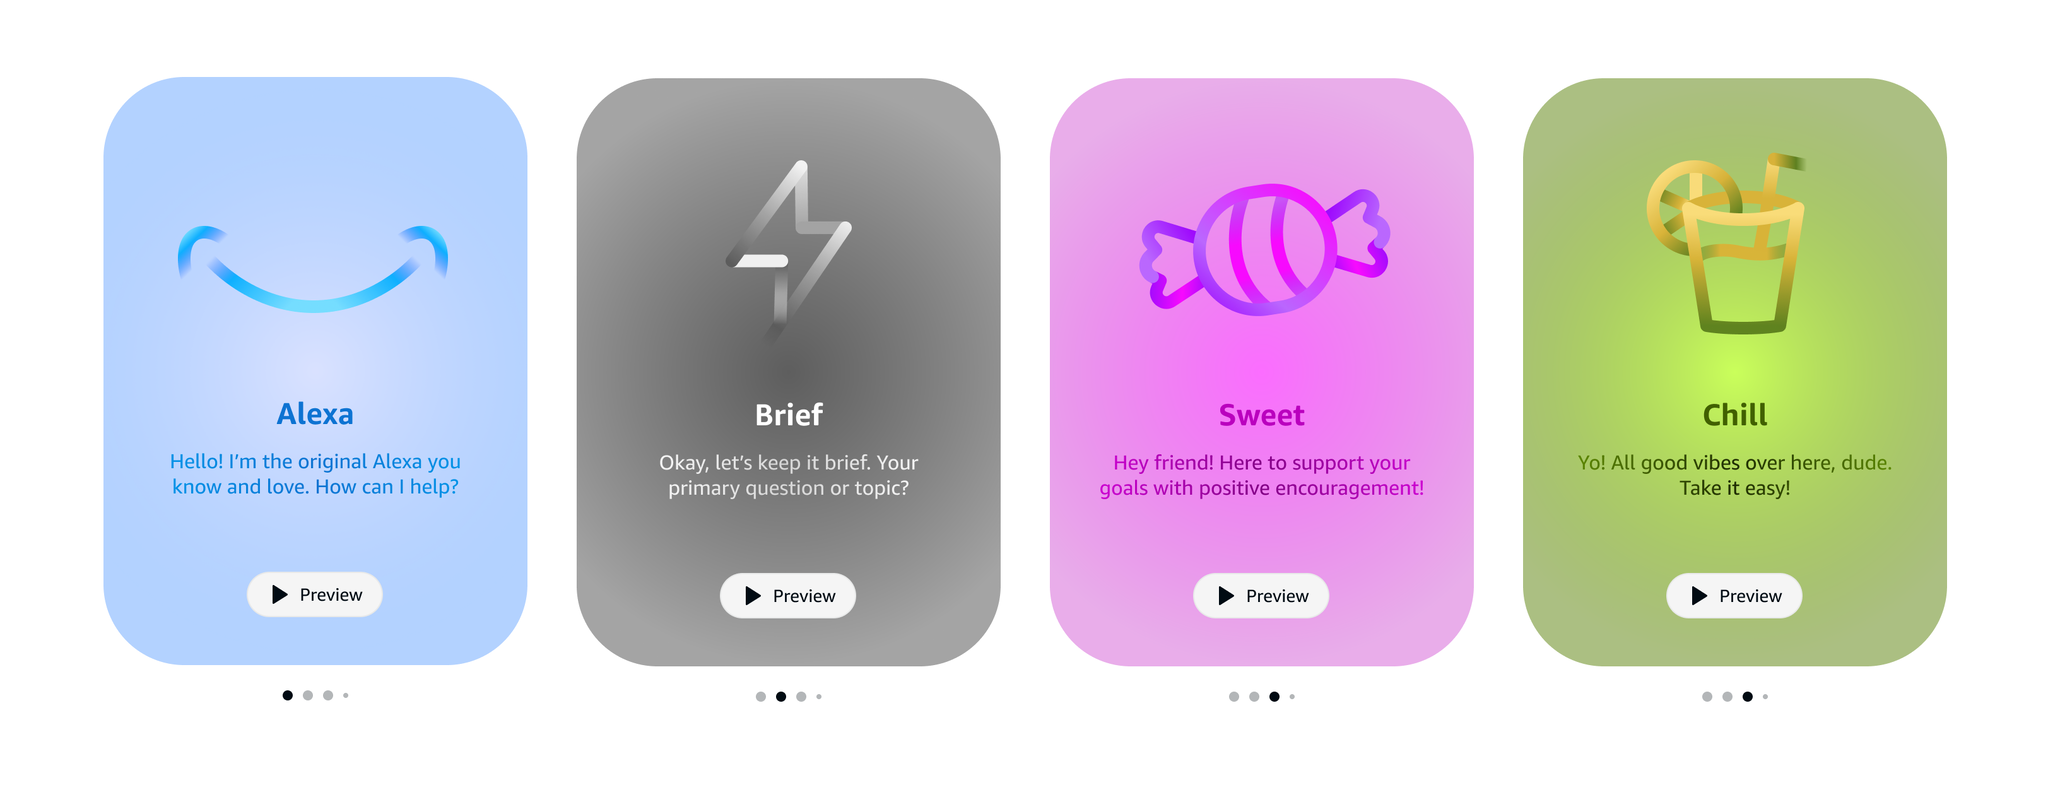
Amazon is offering a new way for Alexa+ users to customize the AI assistant's communication style. The company has introduced three personalities for Alexa+, so the assistant can adopt an attitude that is Brief, Chill or Sweet.
The Brief style will be exactly that: no small talk and no extra conversation. Chill is easygoing and seems to be inspired by caricatures of the surfer/stoner type, while the Sweet mode is almost aggressively perky and chipper. In the audio sample provided, when a user asks "Alexa, how's it going?" the Chill voice responds, "Life’s treating me well – all systems are Zen and the digital universe is spinning in harmony." In contrast, the Sweet one replies, "Absolutely fantastic! I’m radiating pure joy and ready to make your day incredibly amazing!"
The three new personality styles will set alongside the standard Alexa.
Amazon
Amazon explained that the three personality styles are based on five metrics: expressiveness, emotional openness, formality, directness and humor. The company may release additional options with different combinations of those sliding scale traits in the future.
For now, users can swap the assistant's vibe from the Alexa app or with the spoken command, "Alexa, change your personality style." Both approaches can also be used to swap back to the classic Alexa voice. All three personalities are available now for all Alexa+ customers.
This article originally appeared on Engadget at https://www.engadget.com/ai/amazon-introduces-three-personality-styles-for-alexa-140000602.html?src=rss
1Password is increasing prices for its individual and family plans. The individual rate is increasing from nearly $36 a year to $48, while the family option will cost $72 instead of $60. In emails sent to users, the business announced that the new rates will take effect for users at their next subscription renewal after March 27.
It's a sizable price hike, but 1Password hasn't been incrementally inching its fees higher every couple years like we see so often for streaming subscriptions. This is the biggest bump we've seen to its rates in several years, even though the company has been adding ever-more tools for cybersecurity, such as new phishing protections that rolled out last month. Even at the higher cost, it's still one of the best options out there for password management.
Fortunately for those on a budget, we have seen 1Password offer pretty substantial discounts on its plans at times, often cutting the rates by as much as half. The company usually participates in the big deal sprees like Black Friday, but keep an eye out for standalone sales that might pop up year-round.
This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/1password-plans-are-getting-more-expensive-soon-213236400.html?src=rss
A common theme in online age verification laws is the tension between user privacy and preventing children from accessing harmful or inappropriate content. Now the UK is sending a not-so-subtle message to Reddit on the subject, to the tune of £14.5m ($19.6 million). The nation's Information Commissioner's Office (ICO) accused the company of using children’s data and potentially exposing them to inappropriate content.
“Children under 13 had their personal information collected and used in ways they could not understand, consent to or control,” UK Information Commissioner John Edwards wrote in a statement. “That left them potentially exposed to content they should not have seen. This is unacceptable and has resulted in today’s fine.”
In July 2025, Reddit began requiring age verification to access adult content in the UK, in compliance with the Online Safety Act. However, that's only used to block under-18 users from sexually explicit, violent or other mature posts. The platform also prohibits users under 13 from accessing it altogether — and enforcement of that policy is lax. It merely requires users to declare, when signing up, that they're over 13. The ICO (accurately) described the method as "easy to bypass."
In its defense, Reddit told the BBC that it "didn't require users to share information about their identities, regardless of age, because we are deeply committed to their privacy and safety." The company said it would appeal the decision. "The ICO's insistence that we collect more private information on every UK user is counterintuitive and at odds with our strong belief in our users' online privacy and safety," the spokesperson added.
"It's concerning that a company the size of Reddit failed in its legal duty to protect the personal information of UK children," Edwards said. "Companies operating online services likely to be accessed by children have a responsibility to protect those children by ensuring they’re not exposed to risks through the way their data is used. To do this, they need to be confident they know the age of their users and have appropriate, effective age assurance measures in place.”
“Reddit failed to meet these expectations,” he added. “They must do better, and we are continuing to consider the age assurance controls now implemented by the platform.” The ICO also accused Reddit of failing to conduct a data protection impact assessment by January 2025.
The Guardiannotes that the £14.5m fine is the third-largest handed down by the ICO. It trails only a £20m fine for British Airways involving a data breach disclosure and an £18.4m penalty for Marriott Hotels for exposing over 300 million customer records in a hack.
This article originally appeared on Engadget at https://www.engadget.com/social-media/reddit-fined-196-million-over-age-verification-checks-in-the-uk-173705048.html?src=rss
Ring CEO Jamie Siminoff has indicated that the company's controversial Search Party feature might not always be just for lost dogs, according to emails obtained by 404 Media. A creepy surveillance tool being used to surveil. Who could have predicted that?
"I believe that the foundation we created with Search Party, first for finding dogs, will end up becoming one of the most important pieces of tech and innovation to truly unlock the impact of our mission," Siminoff wrote in an email to staffers. "You can now see a future where we are able to zero out crime in neighborhoods. So many things to do to get there but for the first time ever we have the chance to fully complete what we started."
The Ring<->Flock partnership is even worse than imagined, it was setup to be a AI powered mass surveillance system from the start. See this email from the Ring Founder, Jamie Siminoff (https://t.co/kLbZdR6Is1) pic.twitter.com/W9TFQpriRh
The words "zero out crime in neighborhoods" are particularly troubling. It is, however, worth noting that this is just an email and doesn't necessarily indicate a plan by the company. Siminoff wrote the email back in October when Search Party first launched, which was months before the public backlash started. He did end the thread by noting he couldn't "wait to show everyone else all the exciting things we are building over the years to come."
One of those things could be the recently-launched "Familiar Faces" tool, which uses facial recognition to identify people that wander into the frame of a Ring camera. It seems to me that a combination of the Search Party tech, which uses the combined might of connected Ring cameras, with the Familiar Faces tech could make for a very powerful surveillance tool that excels at finding specific individuals.
Siminoff also suggested in an earlier email to staffers that Ring technology could have been used to catch Charlie Kirk's killer by leveraging the company's Community Requests feature. This is a tool that allows cops to ask camera owners for footage, thanks to a partnership with the police tech company Axon.
Ring had planned an expansion of this program via a partnership with a surveillance company called Flock Safety. The companies canceled this partnership after a Super Bowl ad spotlighting the Search Party tool triggered public outcry. Ring didn't cite public sentiment for this decision, rather saying the integration would require "significantly more time and resources than anticipated."
Ring has responded to 404 Media's reporting, saying in an email that Search Party "does not process human biometrics or track people" and that "sharing has always been the camera owner's choice." This response did not provide any information as to what the future will hold for the company's toolset.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/ring-could-be-planning-to-expand-search-party-feature-beyond-dogs-175805706.html?src=rss
YouTube is experiencing an outage across the United States, with users in other countries like Canada, India, the Philippines, Australia and Russia also having problems with accessing the website. The issue seems to have started at around 8 PM Eastern time and reached 338,000 reports on Downdetector before starting to taper down. More users reported having issues accessing the app, but I personally lost access to the web homepage first.
As of 9:22 PM, users are still reporting being unable to access YouTube on Reddit. As of 9:33 PM, users are complaining that they still can’t access the service, though others say it’s back up for them. Some people are reporting partial restoration of service, with the homepage now being accessible but not seeing any recommended videos.
Downdetector also got thousands of reports of Google being down at around 8 PM Eastern time. As of 9:53 PM, Engadget Managing Editor Cherlynn Low reports that both YouTube and Google Home Assistant are still inaccessible for her. As of 10:12PM Eastern, Team YouTube posted on X that the issue has been completely fixed. While it didn’t say why YouTube went down, the team acknowledged the problem before 9PM and posted an update 20 minutes later that its recommendation system was having issues, even though its homepage was back.
Update, February 17, 2026, 10:27 PM ET: YouTube says the issue has been completely fixed.
Update, February 17, 2026, 10:08 PM ET: Updated with reports that certain Google services are also down for some users.
Update, February 17, 2026, 9:34 PM ET: Updated with reports from users.
Update, February 17, 2026, 9:26 PM ET: Updated to correct time of outage, added new countries where it’s out and added new reports of YouTube still being inaccessible.
This article originally appeared on Engadget at https://www.engadget.com/big-tech/youtube-was-down-for-thousands-of-users-in-the-us-020718788.html?src=rss
 Anmelden