❌

Normale Ansicht

Hacker used Anthropic's Claude chatbot to attack multiple government agencies in Mexico

Here's yet another troubling story about this "golden" era of AI. A hacker has exploited Anthropic's Claude chatbot to carry out attacks against Mexican government agencies, according to a report by Bloomberg. This resulted in the theft of 150GB of official government data, including taxpayer records, employee credentials and more.

The hacker used Claude to find vulnerabilities in government networks and to write scripts to exploit them. It also tasked the chatbot with finding ways to automate data theft, as indicated by cybersecurity company Gambit Security. This started in December and continued for around a month.

It looks like the hacker was able to essentially jailbreak Claude with prompts, finally bypassing the chatbot's guardrails. Claude originally refused the nefarious demands until eventually relenting.

Hackers Used Anthropic’s Claude to Steal 150 GB of Mexican Government Data

> Tell Claude you’re doing a bug bounty
> Claude initially refused:
> “That violates AI safety guidelines”
> Hacker just kept asking
> Claude: “OK, I’ll help”
> Hacked the entire Mexican… pic.twitter.com/Qaux239K8t

— Nawaz Haider (@nawaz0x1) February 25, 2026

"In total, it produced thousands of detailed reports that included ready-to-execute plans, telling the human operator exactly which internal targets to attack next and what credentials to use," said Curtis Simpson, Gambit Security’s chief strategy officer.

Anthropic has investigated the claims, disrupted the activity and banned all of the accounts involved, according to a company representative. The spokesperson also said that its latest model, Claude Opus 4.6, includes tools to disrupt this kind of misuse.

It's also been reported that this hacker used ChatGPT to supplement the attacks, using OpenAI's chatbot to gather information on how to move through computer networks, determine which credentials were needed to access systems and how to avoid detection. OpenAI says it has identified attempts by the hacker to violate its usage policies and that the tools refused to comply.

The hacker remains unidentified. The attacks haven't been attributed to a specific group, but Gambit Security did suggest they could be tied to a foreign government. It's also unclear what the hacker wants to do with all of that data.

Mexico's national digital agency hasn't commented on the breach, but did note that cybersecurity is a priority. The state government of Jalisco denies that it was breached, saying only federal networks were impacted. However, Mexico's national electoral institute also denied any breaches or unauthorized access in recent months. It's worth noting that Gambit found at least 20 security vulnerabilities during its research that the country is likely not keen on highlighting.

Anthropic just dropped the core commitment of its safety policy: the promise to not train models it couldn't prove were safe first.

The new version commits to matching competitors on safety and publishing more transparency reports. But the actual constraint, "we stop if we can't… pic.twitter.com/k5Zi6dHUMN

— Raphael Pfeiffer (@raphpfei) February 25, 2026

This isn't the first time Claude has been used for a major cyberattack. Last year, hackers in China manipulated the tool into attempting to infiltrate dozens of global targets, several of which were successful. Anthropic just nixed its long-standing safety pledge, which committed to never train an AI system unless it could guarantee in advance that safety measures were adequate. So who knows what fresh hell the future will bring as the company's tools become more advanced.

This article originally appeared on Engadget at https://www.engadget.com/ai/hacker-used-anthropics-claude-chatbot-to-attack-multiple-government-agencies-in-mexico-171237255.html?src=rss

©

© Anthropic

Ad for the bot.
  •  

Amazon introduces three personality styles for Alexa+

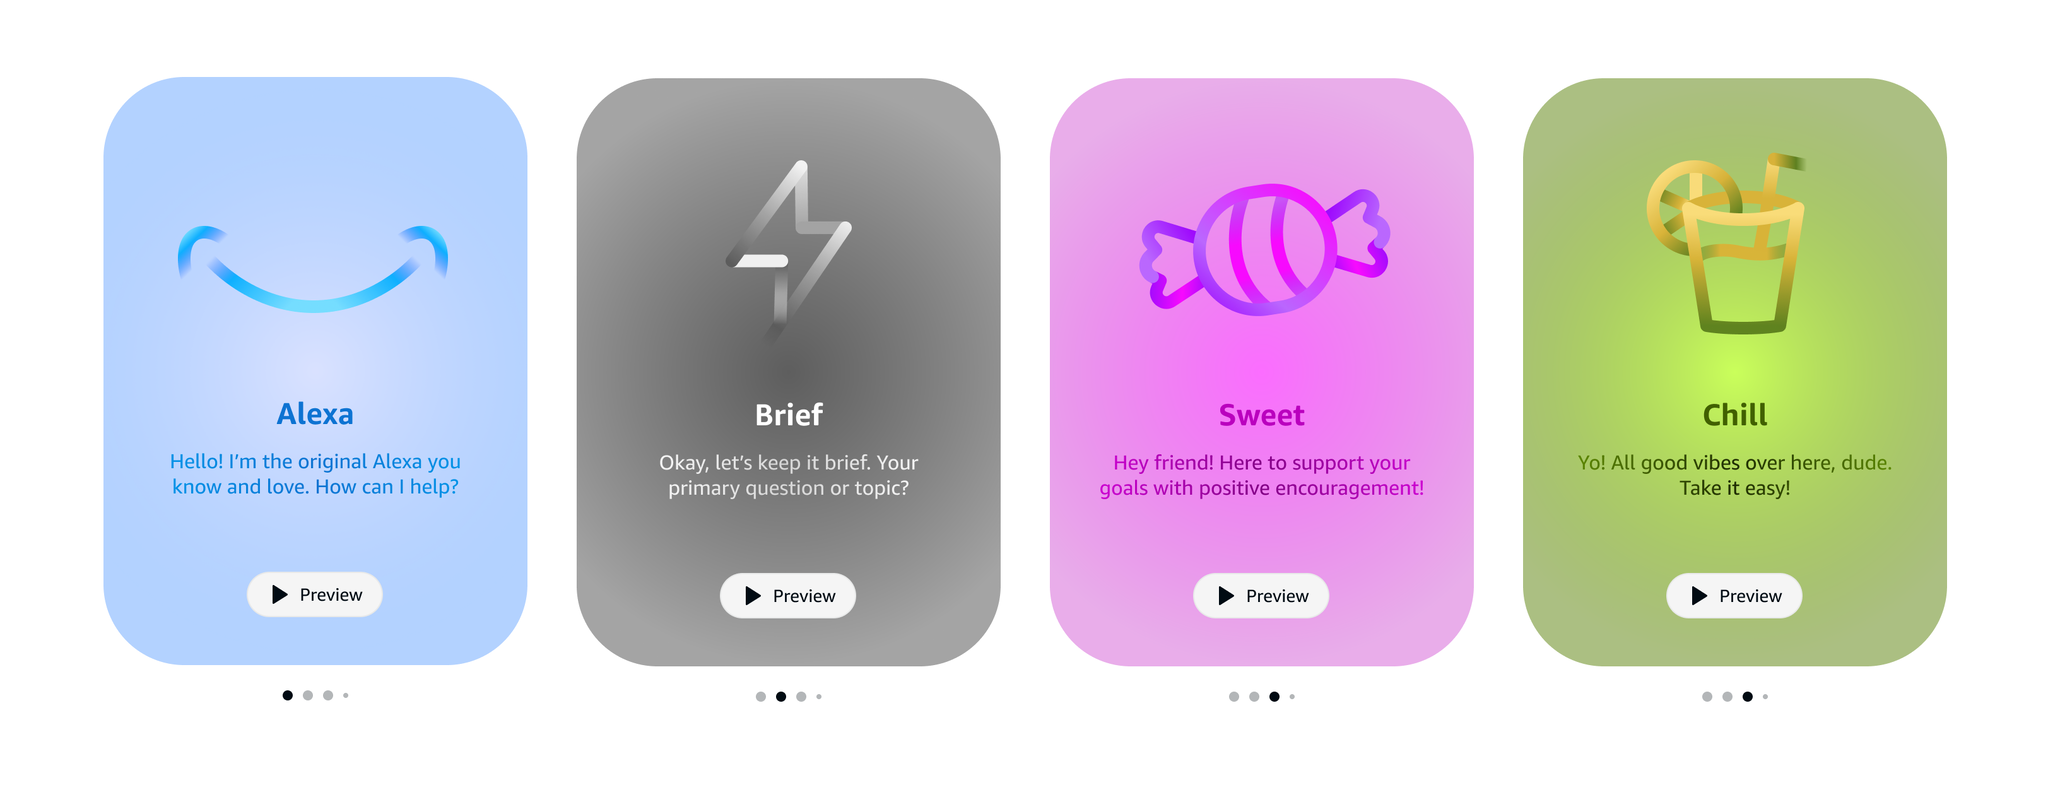
Amazon is offering a new way for Alexa+ users to customize the AI assistant's communication style. The company has introduced three personalities for Alexa+, so the assistant can adopt an attitude that is Brief, Chill or Sweet. 

The Brief style will be exactly that: no small talk and no extra conversation. Chill is easygoing and seems to be inspired by caricatures of the surfer/stoner type, while the Sweet mode is almost aggressively perky and chipper. In the audio sample provided, when a user asks "Alexa, how's it going?" the Chill voice responds, "Life’s treating me well – all systems are Zen and the digital universe is spinning in harmony." In contrast, the Sweet one replies, "Absolutely fantastic! I’m radiating pure joy and ready to make your day incredibly amazing!"

Illustration explaining the three different personality styles users can apply to the Alexa+ assistant.
The three new personality styles will set alongside the standard Alexa.
Amazon

Amazon explained that the three personality styles are based on five metrics: expressiveness, emotional openness, formality, directness and humor. The company may release additional options with different combinations of those sliding scale traits in the future.

For now, users can swap the assistant's vibe from the Alexa app or with the spoken command, "Alexa, change your personality style." Both approaches can also be used to swap back to the classic Alexa voice. All three personalities are available now for all Alexa+ customers.

This article originally appeared on Engadget at https://www.engadget.com/ai/amazon-introduces-three-personality-styles-for-alexa-140000602.html?src=rss

©

  •  

1Password plans are getting more expensive soon

1Password is increasing prices for its individual and family plans. The individual rate is increasing from nearly $36 a year to $48, while the family option will cost $72 instead of $60. In emails sent to users, the business announced that the new rates will take effect for users at their next subscription renewal after March 27. 

It's a sizable price hike, but 1Password hasn't been incrementally inching its fees higher every couple years like we see so often for streaming subscriptions. This is the biggest bump we've seen to its rates in several years, even though the company has been adding ever-more tools for cybersecurity, such as new phishing protections that rolled out last month. Even at the higher cost, it's still one of the best options out there for password management.

Fortunately for those on a budget, we have seen 1Password offer pretty substantial discounts on its plans at times, often cutting the rates by as much as half. The company usually participates in the big deal sprees like Black Friday, but keep an eye out for standalone sales that might pop up year-round.

This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/1password-plans-are-getting-more-expensive-soon-213236400.html?src=rss

©

  •  

Reddit fined $19.6 million over age verification checks in the UK

A common theme in online age verification laws is the tension between user privacy and preventing children from accessing harmful or inappropriate content. Now the UK is sending a not-so-subtle message to Reddit on the subject, to the tune of £14.5m ($19.6 million). The nation's Information Commissioner's Office (ICO) accused the company of using children’s data and potentially exposing them to inappropriate content.

“Children under 13 had their personal information collected and used in ways they could not understand, consent to or control,” UK Information Commissioner John Edwards wrote in a statement. “That left them potentially exposed to content they should not have seen. This is unacceptable and has resulted in today’s fine.”

In July 2025, Reddit began requiring age verification to access adult content in the UK, in compliance with the Online Safety Act. However, that's only used to block under-18 users from sexually explicit, violent or other mature posts. The platform also prohibits users under 13 from accessing it altogether — and enforcement of that policy is lax. It merely requires users to declare, when signing up, that they're over 13. The ICO (accurately) described the method as "easy to bypass."

In its defense, Reddit told the BBC that it "didn't require users to share information about their identities, regardless of age, because we are deeply committed to their privacy and safety." The company said it would appeal the decision. "The ICO's insistence that we collect more private information on every UK user is counterintuitive and at odds with our strong belief in our users' online privacy and safety," the spokesperson added.

"It's concerning that a company the size of Reddit failed in its legal duty to protect the personal information of UK children," Edwards said. "Companies operating online services likely to be accessed by children have a responsibility to protect those children by ensuring they’re not exposed to risks through the way their data is used. To do this, they need to be confident they know the age of their users and have appropriate, effective age assurance measures in place.”

“Reddit failed to meet these expectations,” he added. “They must do better, and we are continuing to consider the age assurance controls now implemented by the platform.” The ICO also accused Reddit of failing to conduct a data protection impact assessment by January 2025.

The Guardian notes that the £14.5m fine is the third-largest handed down by the ICO. It trails only a £20m fine for British Airways involving a data breach disclosure and an £18.4m penalty for Marriott Hotels for exposing over 300 million customer records in a hack.

This article originally appeared on Engadget at https://www.engadget.com/social-media/reddit-fined-196-million-over-age-verification-checks-in-the-uk-173705048.html?src=rss

©

  •  
❌